Cybersecurity Insights & Updates
Stay ahead of cybersecurity threats with expert insights, compliance guides, and industry best practices from our security professionals.
Browse by Category
Find the cybersecurity topics that matter to you
Compliance
SOC 2, HIPAA, ISO 27001 guides
Healthcare
AI, patient data & medical security
Team Insights
Meet our cybersecurity experts
Security Tips
Practical cybersecurity advice
Latest Articles
Fresh insights from our cybersecurity experts
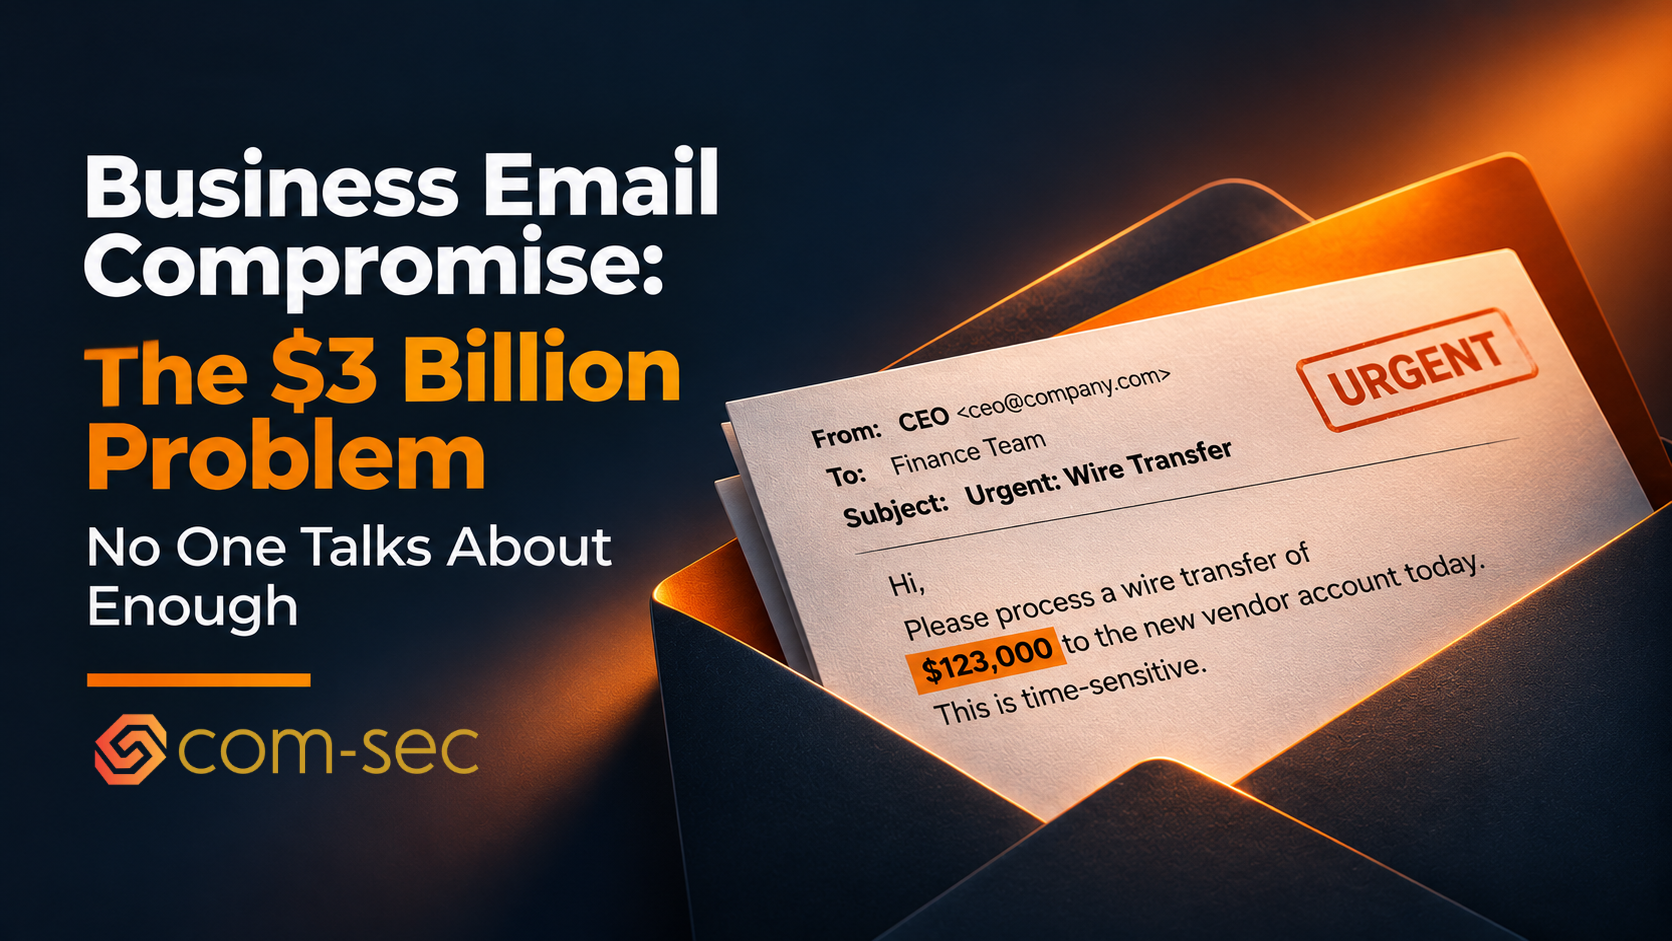
Business Email Compromise: The $3 Billion Problem No One Talks About Enough
Business email compromise is not new. But the numbers keep getting worse, and most companies still aren't treating it like the threat it is.
Zero Trust for Startups: What It Actually Means (Without the Enterprise BS)
Every startup founder thinks zero trust requires a seven-figure budget and a team of 20. It doesn't. Here's what it actually is and what it looks like at a 50-person company.
AICPA SOC 2 Updates: What's Changing and What It Means for You
The AICPA is making changes to SOC 2, and most companies aren't paying attention yet. Here's what's happening and what it means for you.
The White House AI Accord: What It Means for Startups and Why AI Assurance Just Got Real
It's not a law. There are no penalties for non-compliance. But if you're building or deploying AI, this accord is going to affect you — whether you signed it or not.
How to Report Security to Your Board Without Putting Them to Sleep (or Scaring Them)
Either the report is so technical that board members tune out, or it's so high-level that it's meaningless. Neither outcome helps you.
Your Open-Source Dependencies Are Someone Else's Weekend Project. Act Accordingly.
Every modern software company runs on open source. The risk profile has changed significantly, and most companies haven't adjusted.
What Your Cyber Insurance Carrier Is About to Ask You (And Why You Should Care)
Cyber insurance used to be simple. That era is over. Here's what carriers are actually asking now, and what it means for your premium.
Healthcare Breaches Hit 281 in the First Half of 2026. Here's What That Means for Health Tech Startups.
Healthcare data breaches aren't slowing down. They're accelerating. These numbers aren't just industry statistics — they're a preview of the threat landscape you're operating in.
Your AI Agents Are a Security Blind Spot. Here's Why That Matters.
88% of organizations that have deployed AI agents have experienced agent-related security incidents. Here's what breaks when agents go wrong, and what to do about it.
Your Q4 Compliance Planning Checklist (So Q1 Isn't a Scramble)
Every year, the same thing happens. Security and compliance get pushed to January, then suddenly everything is urgent. Q4 is the time to set up Q1 for success.
What the Change Healthcare Breach Should Have Taught Every Health Tech Company
The root cause was almost embarrassingly simple: a Citrix remote access portal without multi-factor authentication.
The HIPAA Security Rule Is Getting Its Biggest Overhaul in 20 Years. Here's What's Actually Changing.
Some companies are treating the delay as permission to wait. That's a mistake. Here's what's actually in the proposed rule, and what to do now.
7 Signs Your Business Needs Fractional Security Leadership
There's a point where the "we'll figure it out" approach to security breaks. Here are the seven signs your company has outgrown it.
What Does a Fractional CISO Do? Roles and Responsibilities
The title sounds impressive, but most founders considering hiring one have the same question: what does this person actually do, week to week?
Why Security Awareness Training Matters for Every Employee
Security awareness training is not going to stop breaches. But it still matters. Here's why, and how to do it in a way that actually provides value.
Cybersecurity Strategy vs. Cybersecurity Roadmap: What's the Difference?
These two terms get used interchangeably. They're not the same thing — and understanding the difference matters.
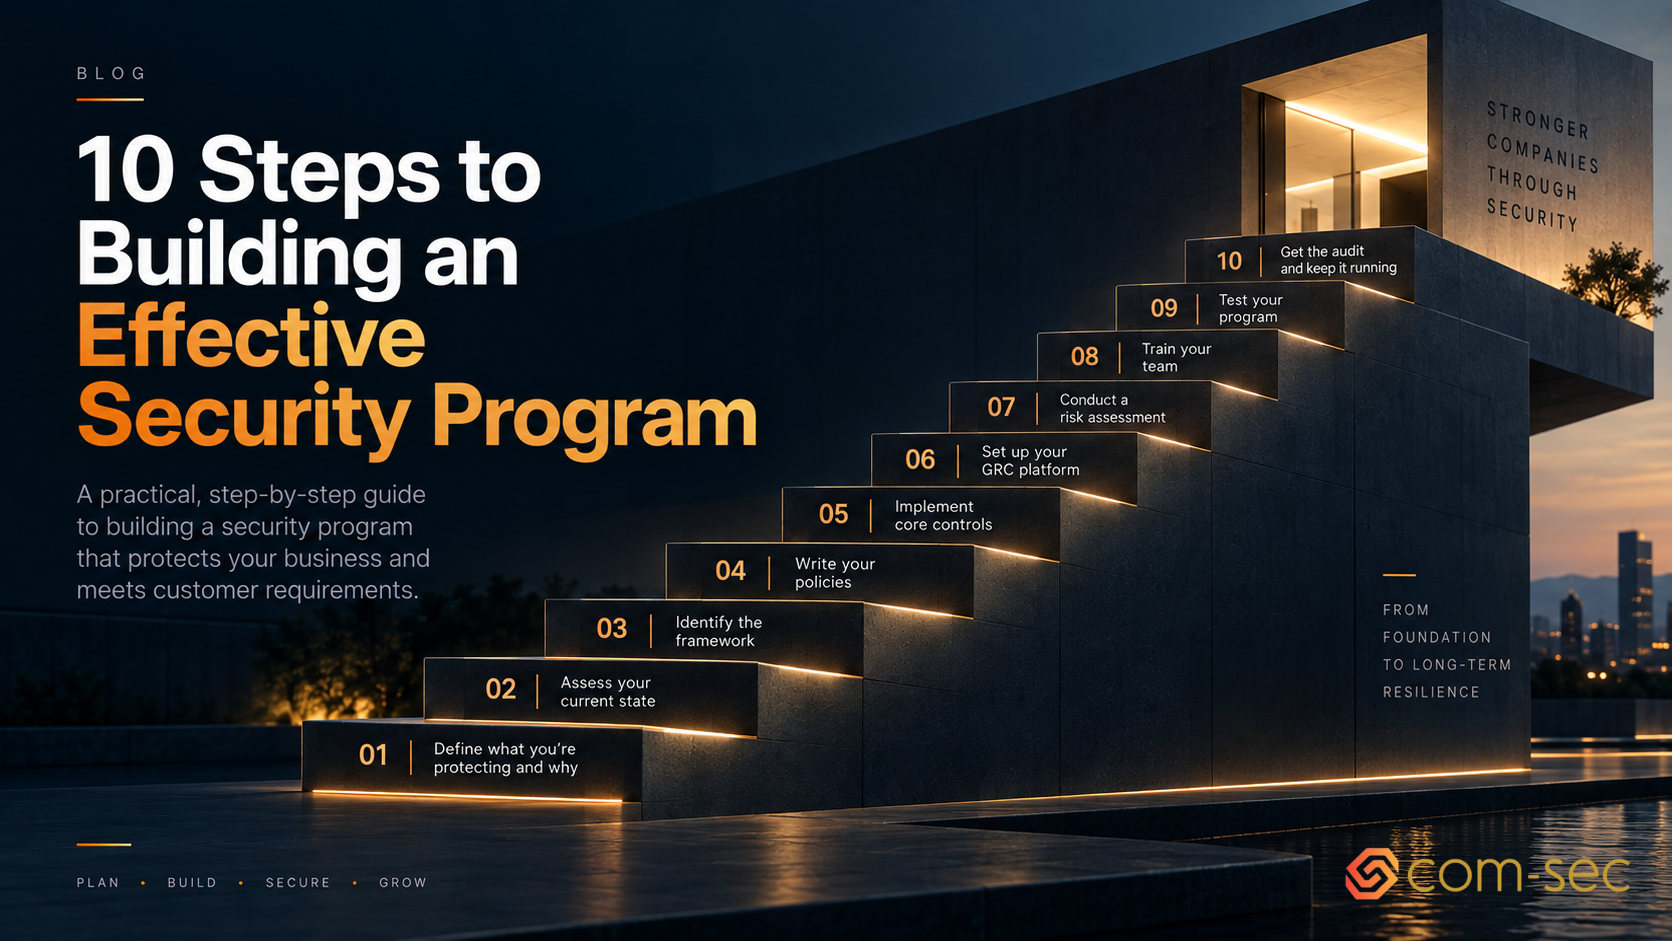
10 Steps to Building an Effective Security Program
Building a security program is a sequence of practical steps that build on each other. Here's the order we use with every client.
How a Fractional CISO Builds a Strong Cybersecurity Strategy
What building a cybersecurity strategy actually looks like in practice - from the first two weeks understanding the business through the risk assessment, roadmap, and ongoing execution.
Introducing Our Security Vulnerability Research Program
Continuous external threat hunting from vetted researchers, included in every vCISO and managed security engagement. You only pay when something real is found.
HITRUST Certification: e1, i1, and r2 Explained
HITRUST is the gold standard for healthcare security certification. Here's the plain English breakdown of the three tiers and which one you actually need.
What 24/7 Security Monitoring Actually Looks Like for a Small Company
Most startups answer “yes” to the 24/7 monitoring question and mean “we have a tool that generates alerts.” Those are two very different things.
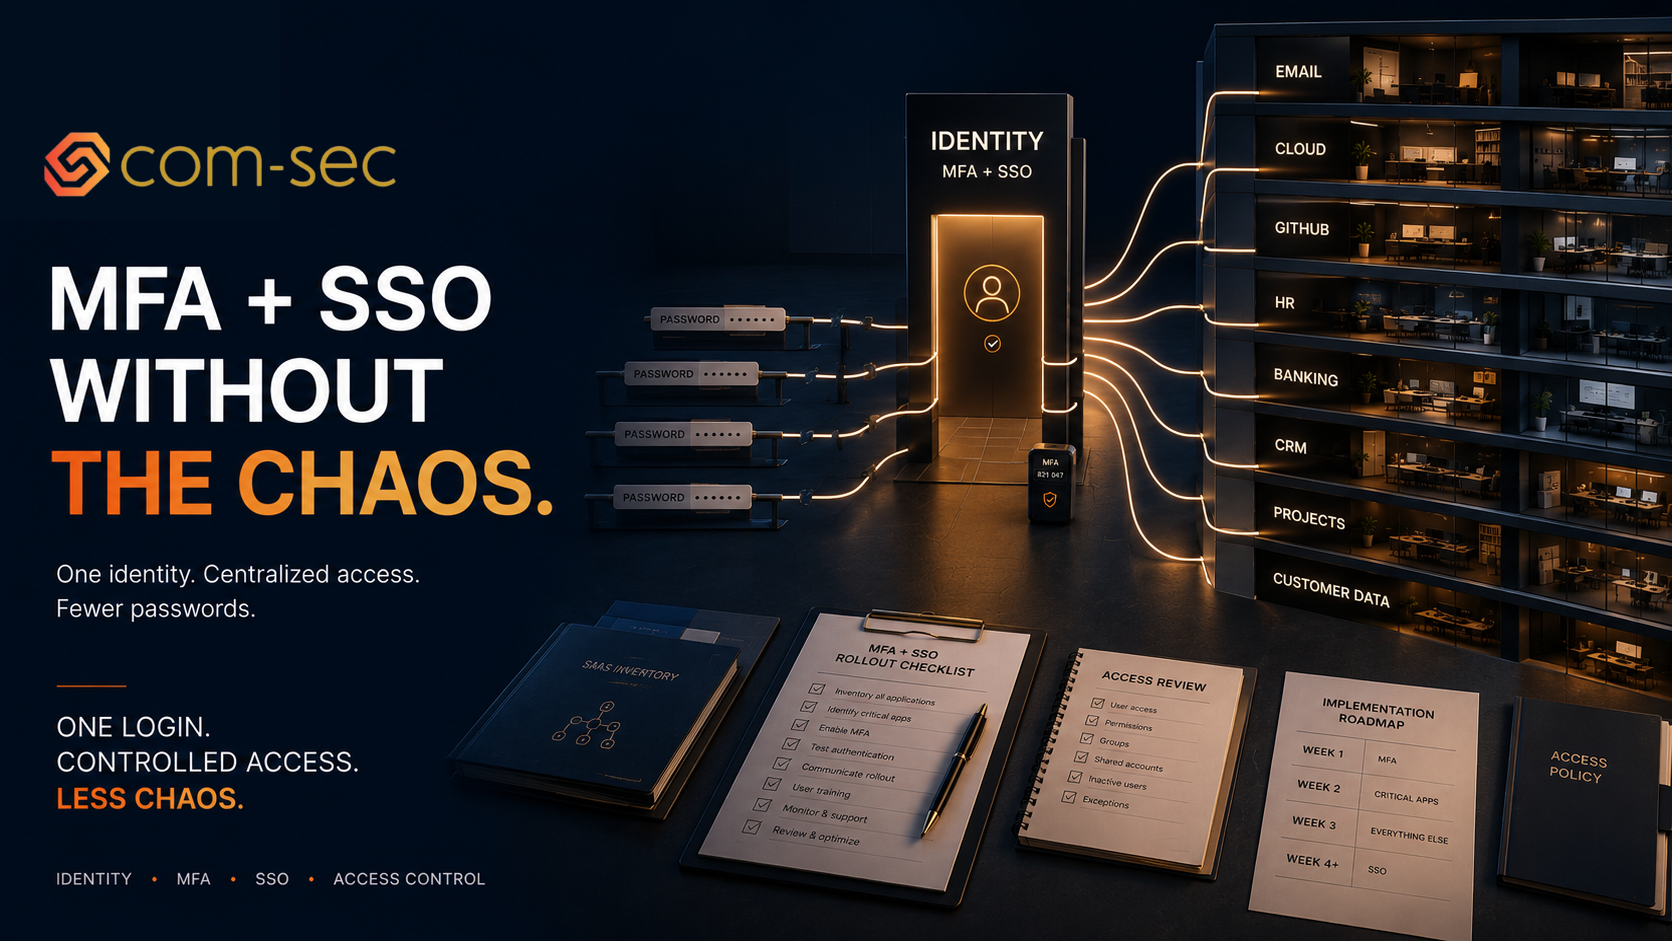
How to Roll Out MFA and SSO Without Losing Your Mind
Every compliance framework requires it. Every enterprise customer asks about it. Most companies still haven't fully deployed MFA and SSO. Here's how to do it without breaking everything.
Your Security Policies Shouldn't Sound Like Everyone Else's
Template policies describe a generic company. Your auditor is evaluating your company. If the policy doesn't match reality, it fails at both jobs.
You Got Your SOC 2. Then You Stopped. Now the Next Audit Is 90 Days Away.
Getting SOC 2 is the hard part. Keeping it is the discipline. Why compliance programs go dormant after the first audit, what the auditor finds when they do, and how to break the cycle.
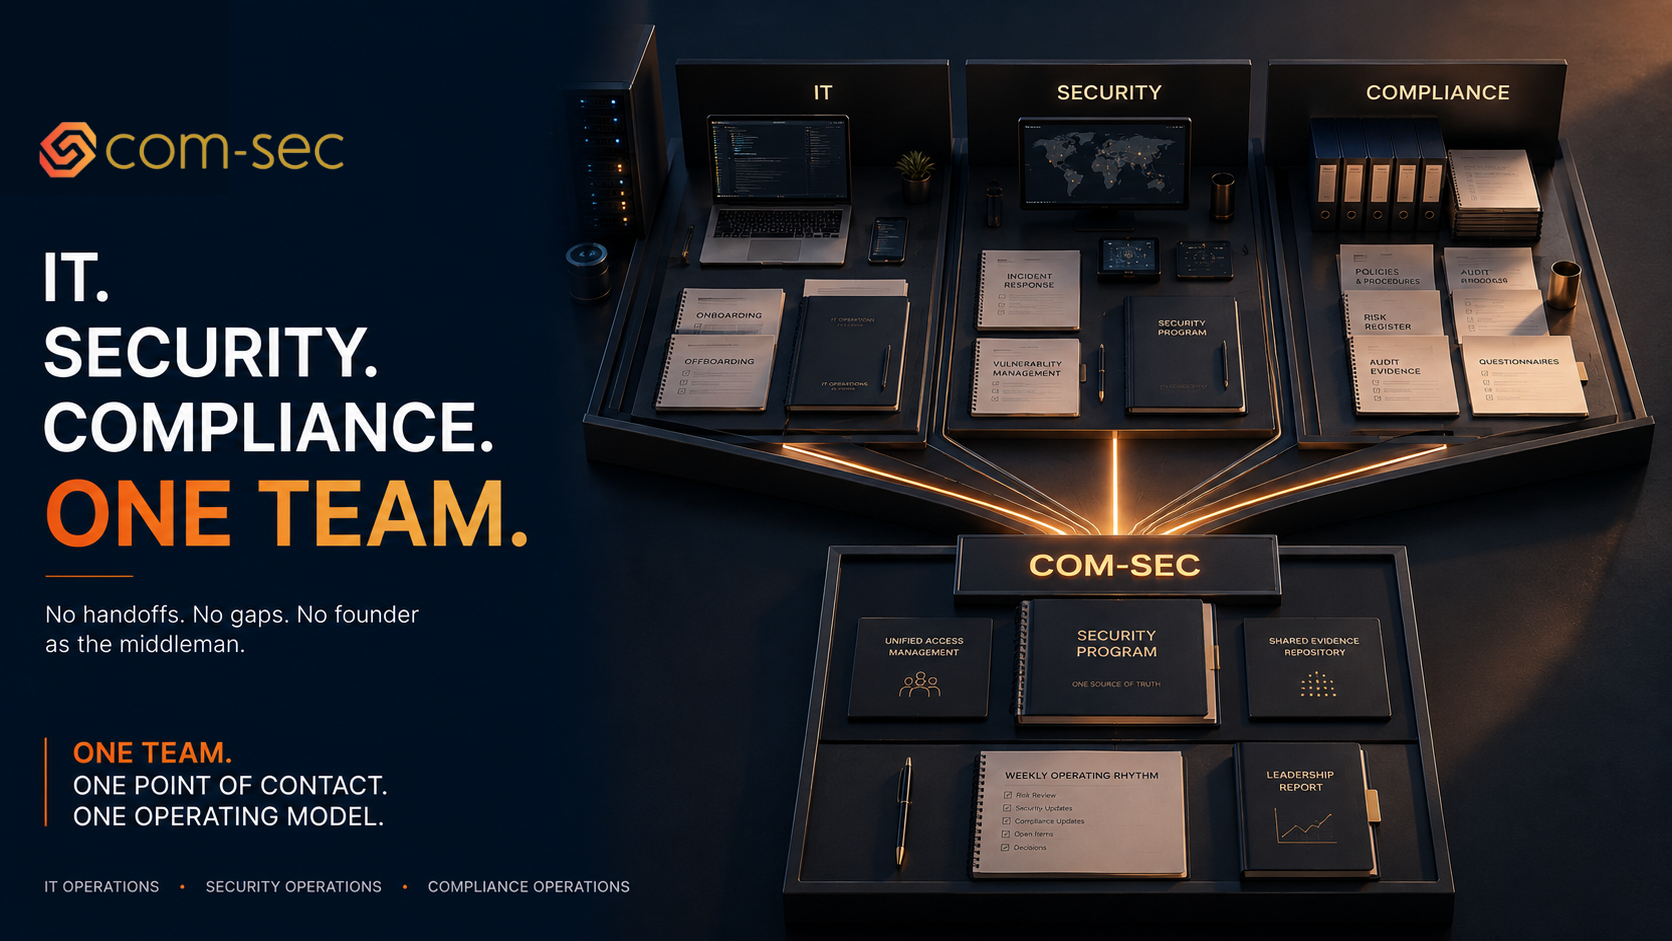
IT, Security, and Compliance Under One Roof: Why It Matters
Three vendors, three invoices, three sets of meetings, and none of them talking to each other. This is the default model and it's broken.
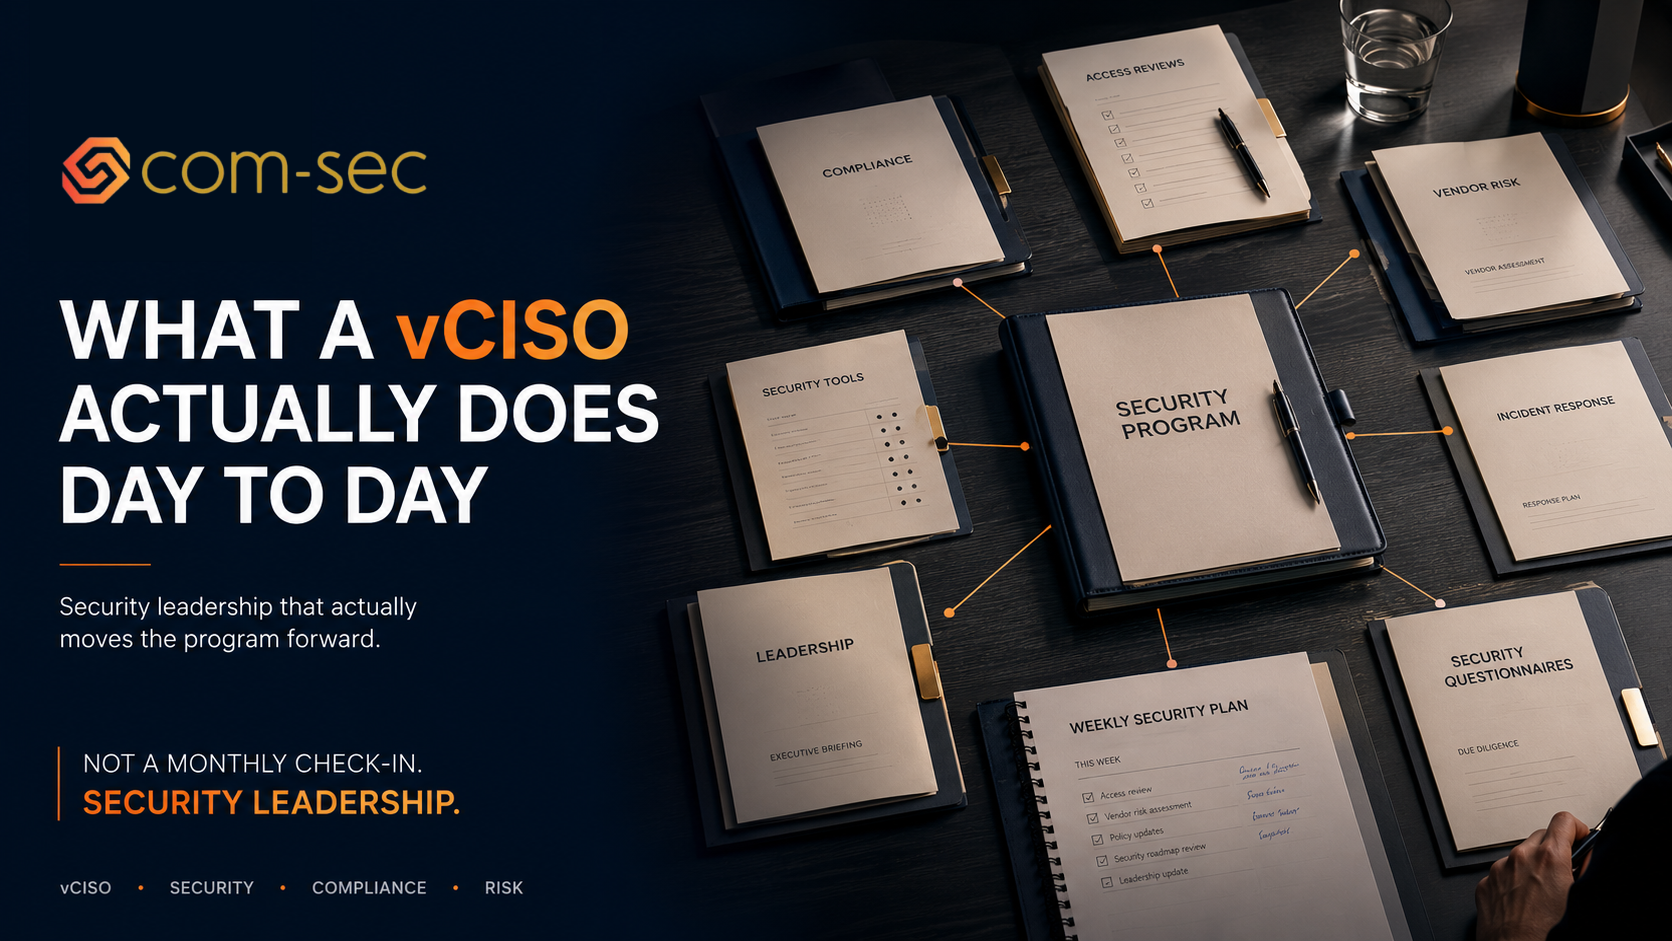
What a vCISO Actually Does Day to Day
Everyone sells vCISO services. Most companies buying one have no idea what they're actually getting. Here's what a vCISO should actually be doing for your company, week to week.
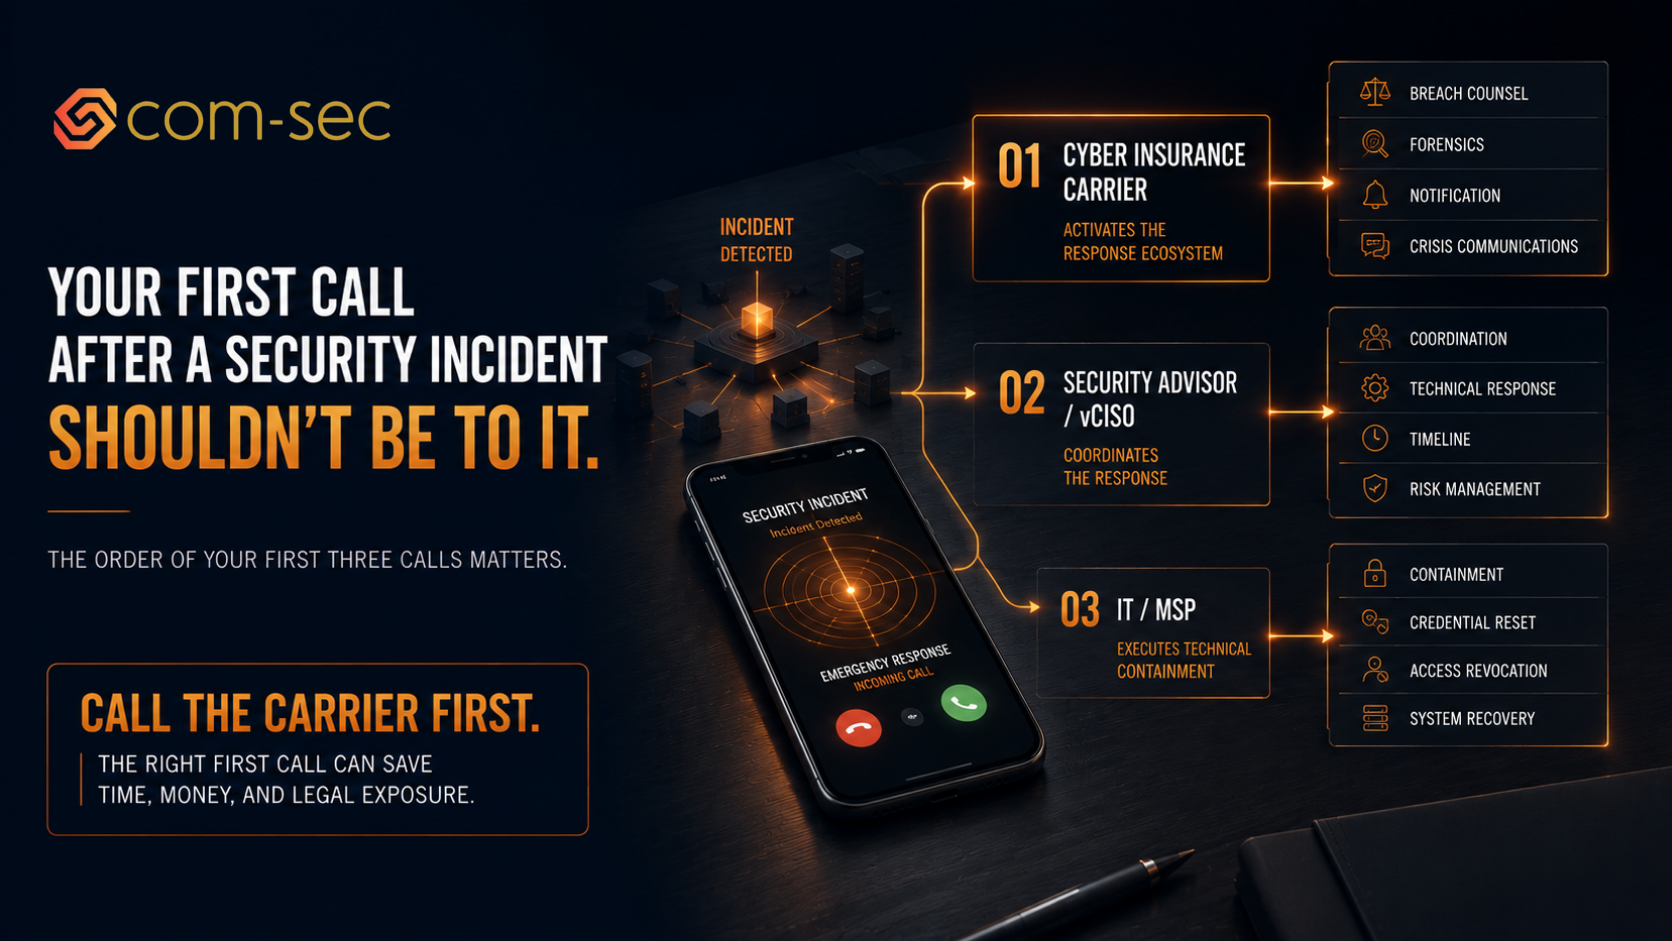
Your First Call After a Security Incident Shouldn't Be to IT
The order of your first three calls matters more than most companies realize. Getting it right can save you tens of thousands of dollars and significantly improve the outcome.
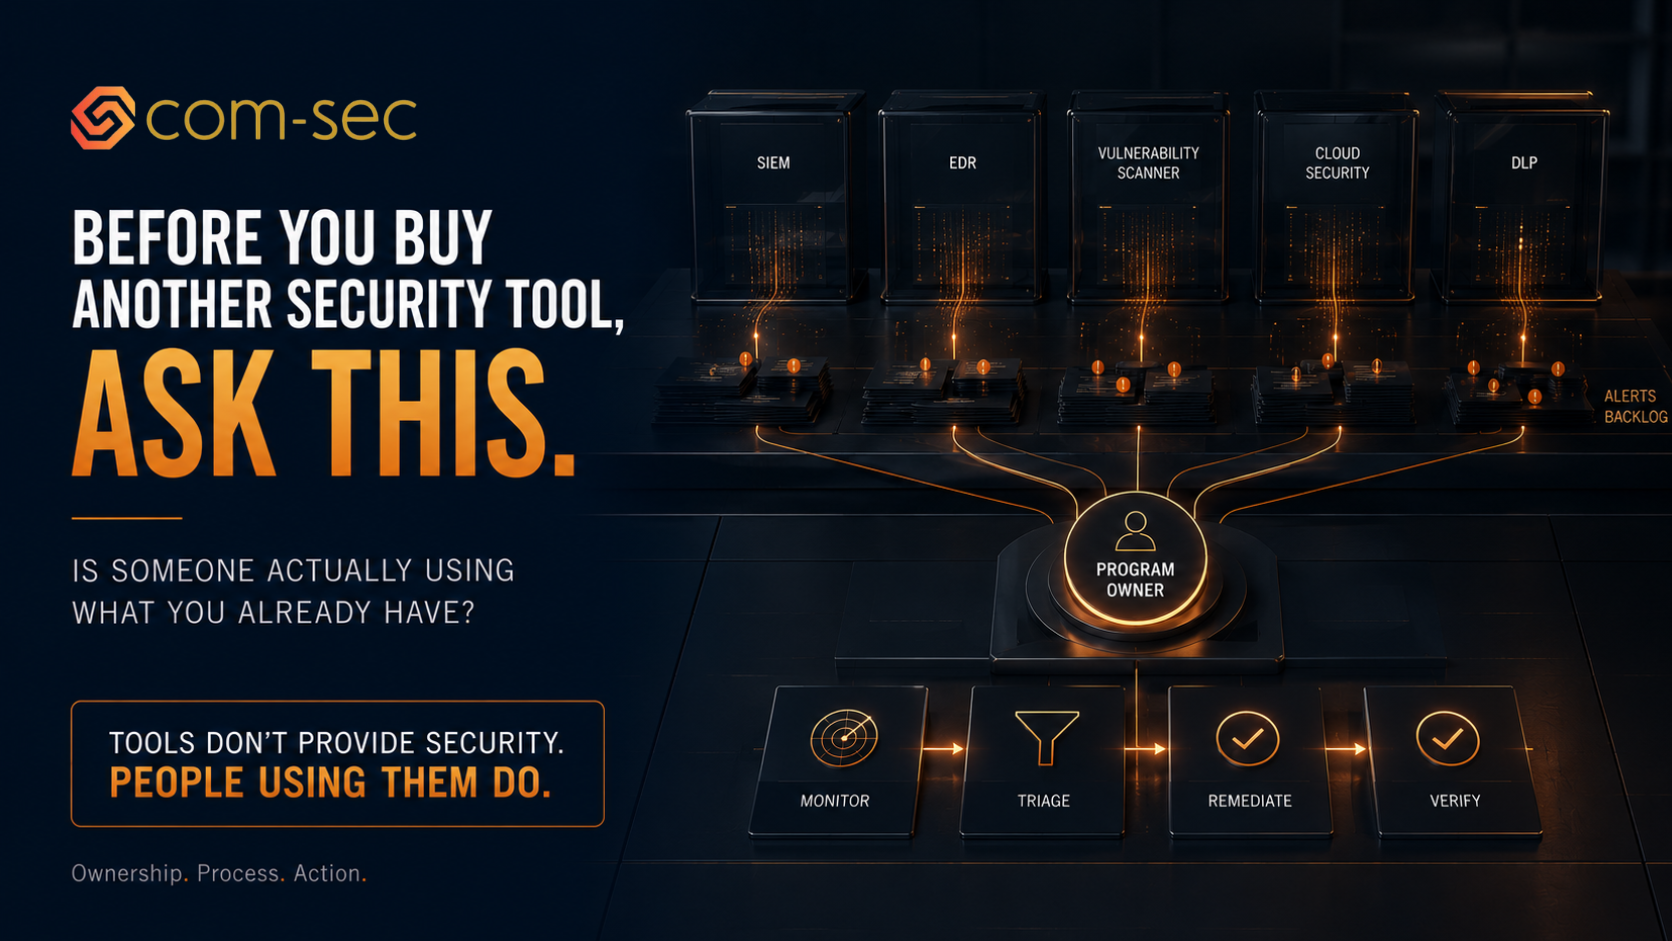
Before You Buy Another Security Tool, Ask This One Question
I've walked into environments with $200,000 in annual security tooling spend and nobody checking the alerts. The tools didn't fail. The process did.
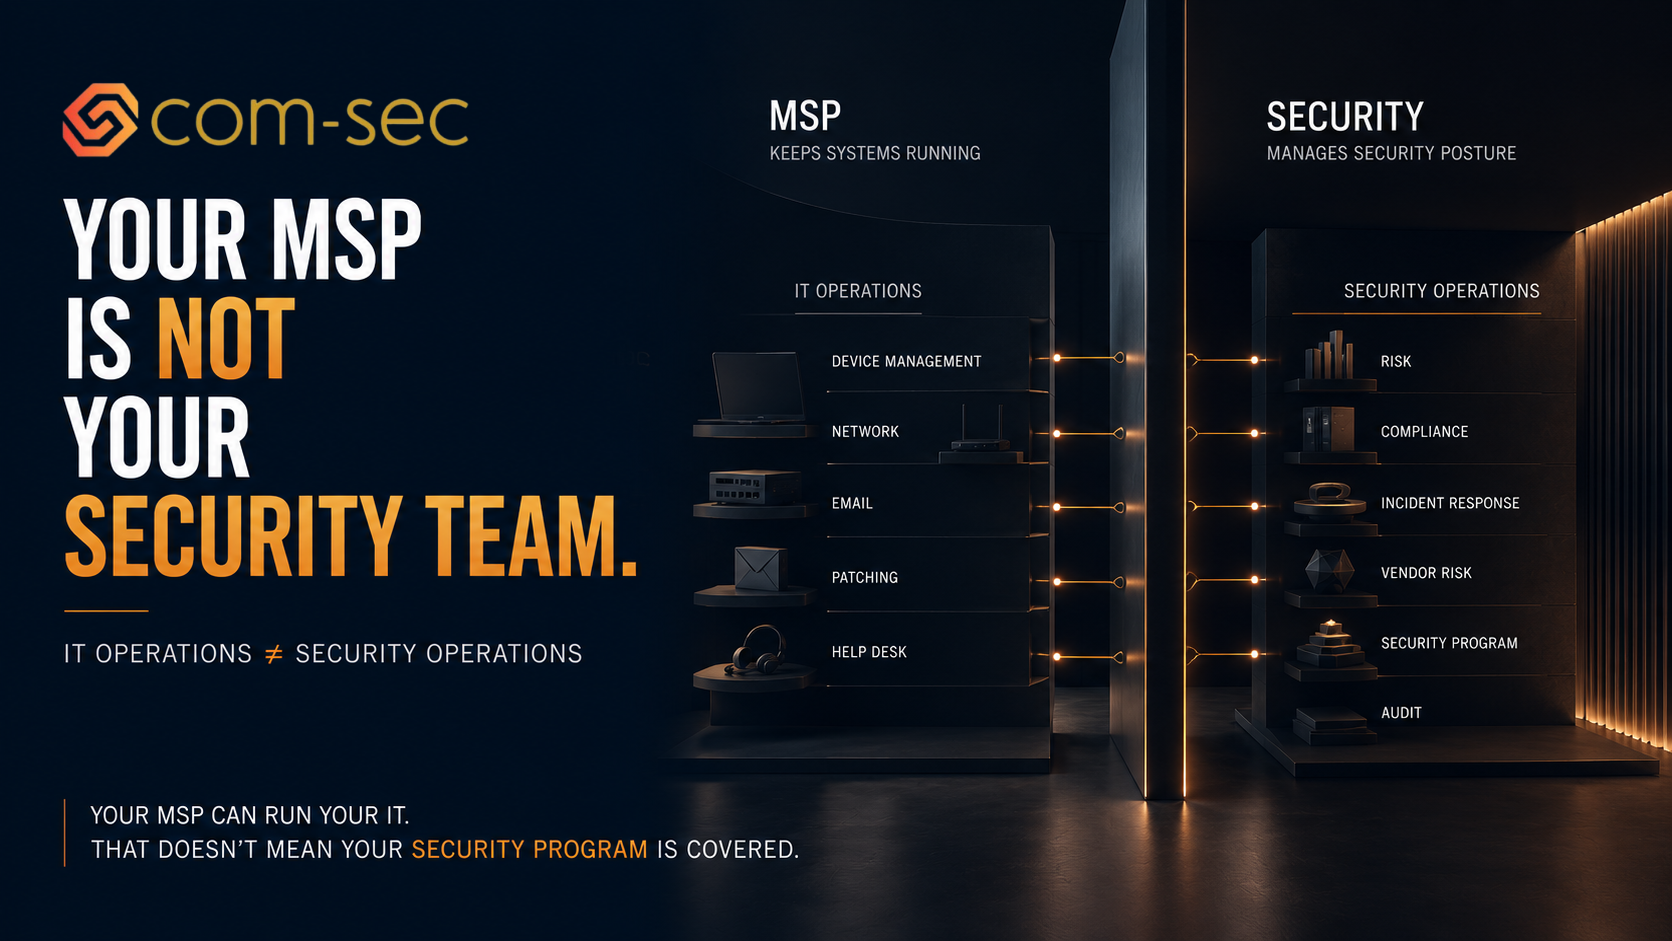
Your MSP Is Not Your Security Team
The confusion between IT operations and security operations is one of the most expensive misunderstandings in small business cybersecurity — and it shows up at the worst possible time.
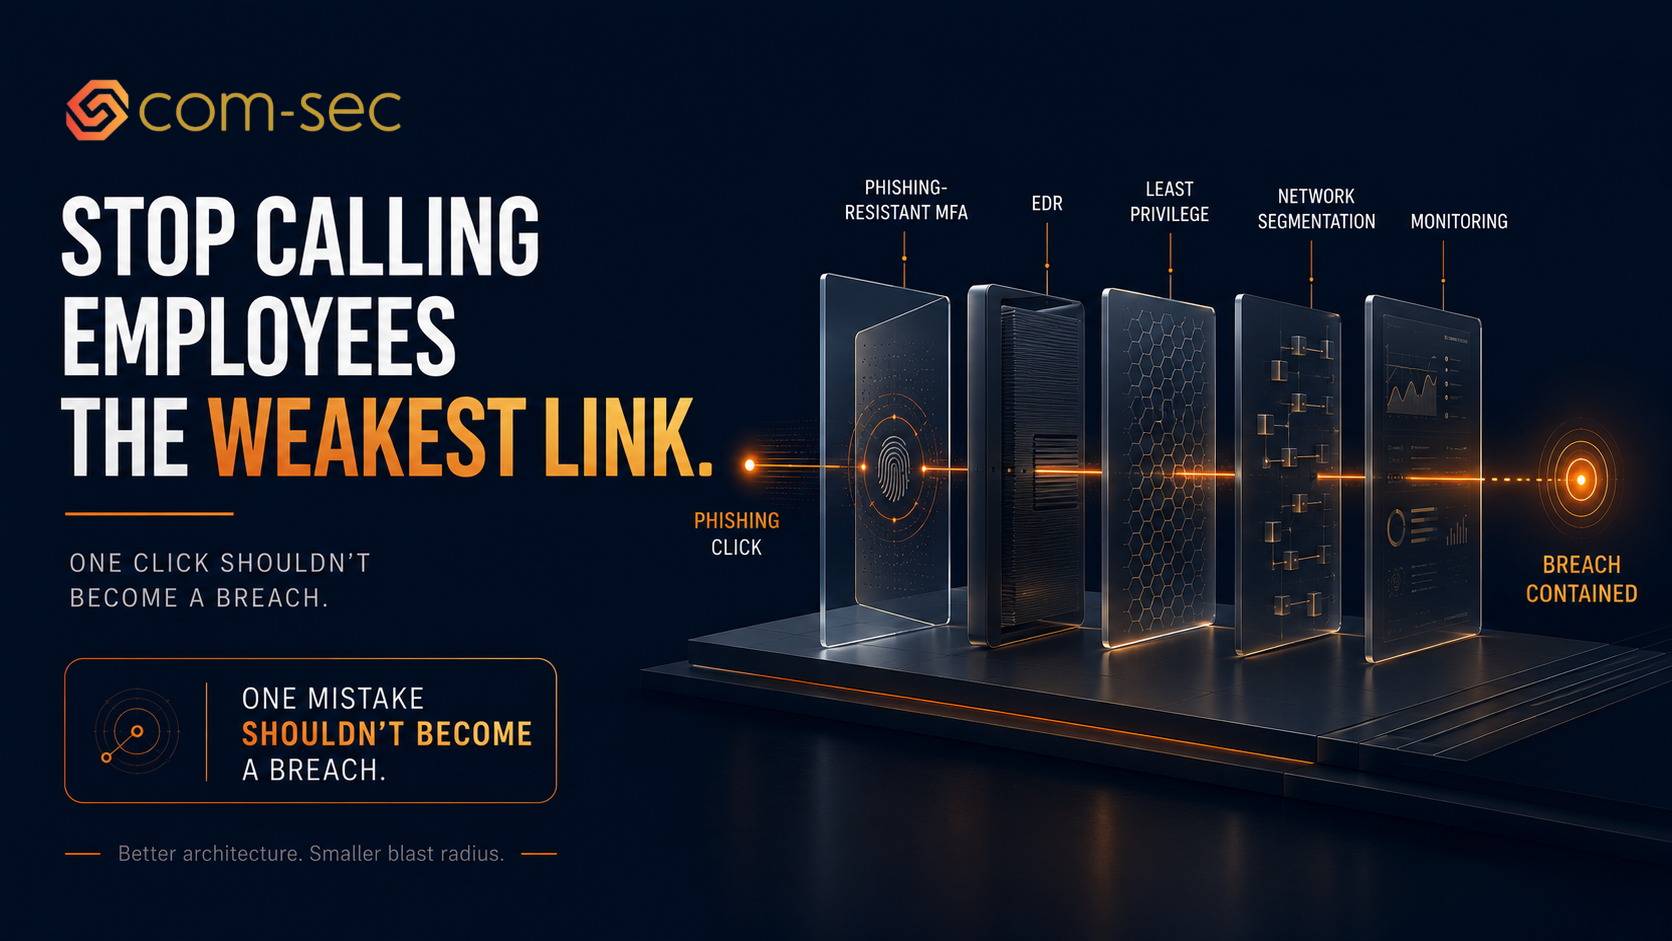
Stop Calling Employees the Weakest Link
If an employee clicks a phishing link and an attacker gets full access to your environment, that's not an employee problem. That's an architecture problem.
Showing 30 of 116 articles